The Expert Take: G7 AI Cybersecurity Drills Explained
In our experience working with hundreds of developers and security engineers, we see firsthand how global policy and industry standards directly affect the everyday realities of tech careers. The G7’s announcement to launch exercises targeting AI-driven cyberattacks signals a pivotal moment in cybersecurity practice—and in the skills companies will soon demand from you. Having trained engineers for both enterprise and government clients, we know that when world leaders take coordinated action, it’s not just news—it’s your next interview question and the benchmark for your technical growth.
What Happened & Why It Matters
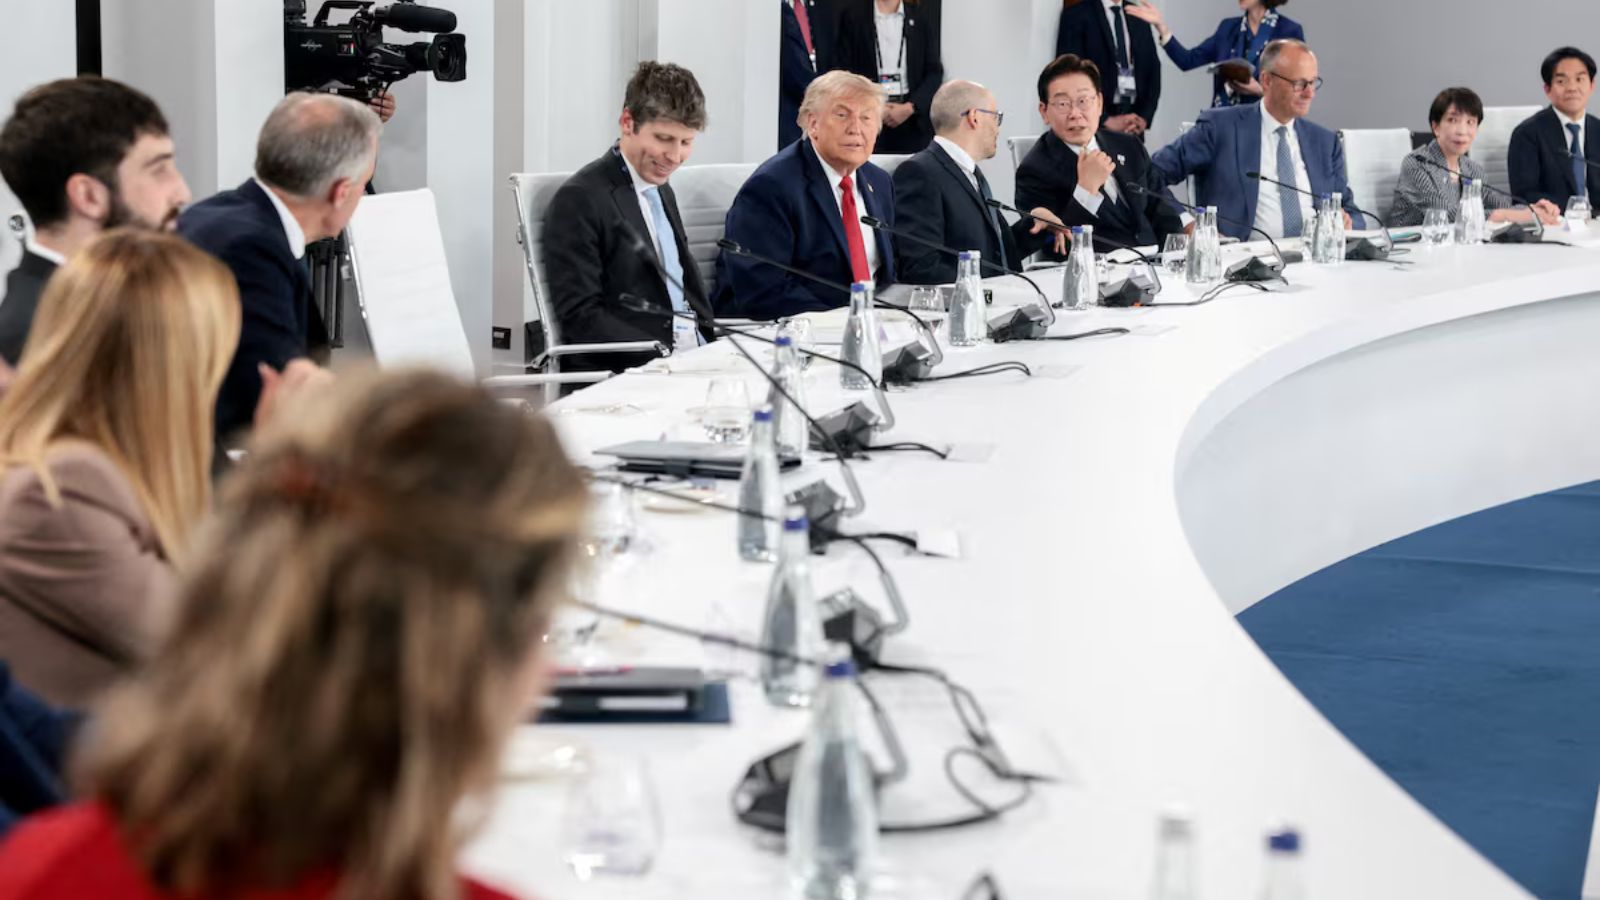
The Group of Seven (G7)—which includes Canada, France, Germany, Italy, Japan, the UK, and the US—has announced a collaborative initiative to conduct exercises aimed at combating AI-powered cyber attacks. This move is a direct response to the surge in malicious actors leveraging generative AI for sophisticated phishing, malware creation, and automated exploitation. According to a 2023 report from IBM, AI-assisted cyberattacks have already increased incident response costs by 27% year-over-year (IBM Security).
The G7’s drills are expected to simulate real-world attack scenarios, where adversaries use AI to breach critical infrastructure, manipulate data, or evade traditional detection tools. By setting a precedent for coordinated defensive exercises, the G7 is essentially laying the groundwork for new international standards on AI security. For developers and security professionals, this means a shift toward more proactive, AI-aware defense architectures—and a growing expectation to be fluent in both offensive and defensive AI techniques.
The Technical Reality: What Engineers Need to Know
AI-driven cyberattacks represent a paradigm shift from traditional threat models. Attackers are now deploying advanced machine learning algorithms to craft spear-phishing emails, bypass authentication mechanisms, and automatically probe for vulnerabilities at scale. For example, GPT-4 can generate convincing phishing content with minimal human oversight, while adversarial networks can manipulate image or text classifiers used in authentication and fraud detection (Stack Overflow).
From an architectural perspective, defending against AI-based threats requires a multi-layered approach. Engineers must consider:
- Integrating AI-based anomaly detection tools (e.g., TensorFlow 2.x, Scikit-learn for real-time log analysis)
- Deploying adversarial training methods to harden models against manipulation (for label smoothing,
tf.keras.utils.to_categorical()for robust loss calculation)torch.nn.CrossEntropyLoss() - Implementing Zero Trust Architecture (NIST SP 800-207), which treats every access attempt—human or AI—as potentially adversarial
- Leveraging AI explainability tools (e.g., SHAP, LIME) to audit model decisions and detect abnormal behavior
Current solutions like traditional SIEM (Security Information and Event Management) systems are often insufficient against AI-driven attacks, which can mutate faster than signature-based detection tools. The rise of AI-powered offensive tools means that defensive systems must adapt by incorporating continual learning and model updating. For example, consider an automated log analysis pipeline:
import tensorflow as tf
from sklearn.ensemble import IsolationForest
Example: anomaly detection in system logs
model = IsolationForest(n_estimators=100)
data = load_log_data()
model.fit(data)
anomalies = model.predict(data)
Such pipelines should be coupled with adversarial validation—a process where synthetic attacks are generated and tested against your defense. Additionally, engineers must now account for the possibility that attackers can manipulate the input distribution of deployed models, requiring robust input validation and integrity checks at every layer of the stack.
The G7’s exercises will likely set new baselines for incident response: automated threat intelligence sharing (using standards like STIX and TAXII), coordinated red/blue team drills, and the adoption of AI-powered defense orchestration platforms. This means you’ll need to understand not just how to build AI models, but how to secure them, audit them, and respond to their failures in production.
Why This Directly Impacts Your Tech Career
If you’re aiming for roles like Security Engineer, DevSecOps Specialist, AI/ML Engineer, or Incident Response Analyst, the G7’s initiative is reshaping job descriptions overnight. Employers will prioritize candidates who understand both the offensive and defensive use of AI in cybersecurity. In the next 12-24 months, expect a surge in demand for skills such as adversarial ML, automated threat detection, and AI model auditing.
Industries most affected include fintech (where fraud prevention is mission-critical), healthtech (with patient data protection), and critical infrastructure (energy, transportation, government). These sectors will be looking for engineers who can not only build robust AI systems but also anticipate and mitigate AI-enabled attacks. According to the 2024 Cybersecurity Jobs Report by CyberSeek, salaries for AI-savvy security engineers are already trending 18% higher than their peers, with median compensation reaching $135,000 in the US (CyberSeek).
For early-career professionals, this is a unique opportunity: the intersection of AI and security is still emerging, so mastering these skills now places you ahead of the curve. The G7’s exercises will set new benchmarks, and companies will look for candidates who can demonstrate hands-on experience with AI-powered attack simulation, defense orchestration, and response automation. If you can articulate how to defend against AI-driven threats in interviews or code reviews, you’ll be on the short list for the most competitive roles.
Skills You Should Build Right Now
- Adversarial Machine Learning – With attackers using AI to evade detection, you need to understand how to defend and stress-test ML models. Start with the “Adversarial Robustness Toolbox” from MITRE and explore hands-on exercises in adversarial training.
- AI-powered Threat Detection – Learn to build and deploy anomaly detection systems using TensorFlow, Scikit-learn, or PyTorch. Begin by completing the “AI for Cybersecurity” course on Coursera.
- Zero Trust Security Architecture – The G7’s coordinated response means Zero Trust will become a global standard. Study NIST’s SP 800-207 and implement micro-segmentation in your cloud projects.
- Incident Response Automation – Practice designing automated playbooks using tools like SOAR (Security Orchestration, Automation, and Response). Try building a Splunk or Sentinel integration for threat response.
- AI Explainability and Auditing – To defend against manipulated AI decisions, learn SHAP and LIME for auditing models. Complete the official SHAP documentation walkthrough and apply it to a fraud detection case.
- Secure Model Deployment – Understand how to deploy hardened models with input validation and integrity checks. Start with OWASP’s Machine Learning Security guidelines and deploy a model to AWS SageMaker with custom validation logic.
Interview Preparation: Questions to Expect
- What are the main vulnerabilities introduced by AI in cybersecurity systems?
Show your understanding of adversarial attacks, automated exploitation, and model manipulation. Reference real-world incidents, such as AI-generated phishing campaigns. - How would you implement adversarial training for an ML model used in fraud detection?
Discuss code-level details, tools (e.g., PyTorch, TensorFlow), and practical steps for hardening models against adversarial inputs. - Describe a time you responded to a cyber incident involving AI or automation.
Be ready to share a behavioral example, focusing on teamwork, escalation, and learning outcomes. If you haven’t faced this directly, outline a hypothetical response based on best practices. - How do you audit an AI model for abnormal behavior in a production environment?
Mention tools like SHAP or LIME, integration with monitoring systems, and your approach to explainability and root-cause analysis.
Support Me Techs Perspective
At Support Me Techs, we’ve seen firsthand that security is no longer just about firewalls and passwords—it’s about defending against algorithms that can adapt, learn, and exploit at scale. Our teaching approach emphasizes real-world labs and red/blue team simulations, where students build and attack AI systems side by side. We believe the G7’s initiative is a wake-up call: if you’re not learning to both build and break AI, you’re falling behind. Our mentorship model pairs students with active security practitioners, ensuring you’re not just learning theory but practicing the same techniques used in industry today.
3 Things You Can Do This Week
- Download and experiment with MITRE’s Adversarial Robustness Toolbox; run basic adversarial attacks on a sample classifier.
- Read NIST’s SP 800-207 Zero Trust Architecture guide and map out a Zero Trust plan for your current or future project.
- Complete the SHAP tutorial on GitHub and apply it to a real dataset to audit model decisions for anomalies.
Frequently Asked Questions
How do AI-powered cyberattacks differ from traditional threats?
AI-powered cyberattacks leverage machine learning algorithms to automate targeting, generate convincing phishing messages, and adapt tactics in real time. Unlike traditional threats—which often rely on static payloads or manual exploitation—AI-driven attacks can mutate, learn from defenses, and exploit vulnerabilities at scale. This requires defenders to use AI-enhanced detection and response strategies to keep up with the evolving threat landscape.
What skills are most important for defending against AI-enabled attacks?
The top skills include adversarial machine learning, AI-powered threat detection, Zero Trust Architecture, incident response automation, and AI model auditing. Developing expertise in these areas means you can build, test, and secure intelligent systems against new attack vectors. Start by learning hands-on with tools like TensorFlow, MITRE’s Adversarial Robustness Toolbox, and SHAP, and stay updated with standards from NIST and industry resources like CyberSeek.
Will G7’s AI cybersecurity exercises change hiring requirements?
Yes, the G7’s coordinated effort is likely to set new international benchmarks for AI security skills. Organizations will increasingly seek candidates who can demonstrate experience with AI-driven attack simulations, robust defense architectures, and automated incident response. This will elevate the importance of certifications, hands-on labs, and practical experience with AI in security engineering roles across industries such as fintech, healthtech, and government.
Want to read more?
This is a summary of the article. You can read the full story on the original publisher's website.
Read Full Article